Cybersecurity Software Solutions: Protecting Your Data from 2026’s Top 3 Threats
Anúncios
In an increasingly interconnected world, the digital landscape evolves at an unprecedented pace, bringing with it both innovation and new vulnerabilities. As we look towards 2026, the threats to our digital assets are becoming more sophisticated, pervasive, and challenging to combat. Organizations and individuals alike face a constant barrage of cyber-attacks, ranging from data breaches and ransomware to state-sponsored espionage and advanced persistent threats (APTs). The need for robust cybersecurity software solutions has never been more critical. This comprehensive guide will delve into the top three evolving cyber threats anticipated in 2026 and explore the cutting-edge cybersecurity software solutions designed to protect your invaluable data.
Anúncios
The digital frontier is a battleground, and remaining complacent is no longer an option. Proactive defense and an understanding of the enemy’s tactics are paramount. Our focus here is to equip you with the knowledge to select and implement effective cybersecurity software solutions that stand resilient against the sophisticated attacks of tomorrow.
The Evolving Threat Landscape: 2026’s Top 3 Cyber Threats
To effectively deploy cybersecurity software solutions, one must first understand the nature of the threats they are designed to counter. The year 2026 is projected to bring forth a new generation of cyber dangers, characterized by their stealth, complexity, and potential for widespread damage. Here are the top three:
Anúncios
1. AI-Powered & Autonomous Attacks
The rapid advancement of Artificial Intelligence (AI) and Machine Learning (ML) is a double-edged sword. While these technologies offer immense potential for enhancing cybersecurity defenses, they also empower attackers to launch more sophisticated and autonomous assaults. AI-powered attacks can learn, adapt, and operate with minimal human intervention, making them incredibly difficult to detect and mitigate using traditional methods. We’re talking about:
- Autonomous Malware: Malware that can independently identify vulnerabilities, adapt its attack vectors, and spread across networks without human guidance. This includes polymorphic malware that constantly changes its code to evade detection.
- Deepfake Phishing & Social Engineering: AI-generated voice and video can create highly convincing deepfakes, making it almost impossible for individuals to discern legitimate communications from malicious ones. Attackers can impersonate executives, colleagues, or trusted institutions with unparalleled realism, leading to massive data breaches and financial fraud.
- Automated Vulnerability Exploitation: AI algorithms can rapidly scan for and exploit zero-day vulnerabilities or misconfigurations across vast networks, dramatically reducing the window of opportunity for defenders to patch systems.
The sheer speed and scale at which these AI-driven threats can operate demand equally advanced cybersecurity software solutions capable of real-time analysis and autonomous response.
2. Supply Chain Compromise 2.0
Supply chain attacks are not new, but in 2026, they are expected to evolve into a far more insidious and widespread threat. Attackers are increasingly targeting the weakest links in an organization’s extended supply chain – smaller vendors, third-party software providers, or even open-source components – to gain access to larger, more secure targets. The SolarWinds attack was a stark reminder of this vulnerability, and we anticipate an escalation in sophistication:
- Software Bill of Materials (SBOM) Manipulation: Attackers might inject malicious code directly into open-source libraries or commercial software components, making it incredibly difficult to trace the origin of the compromise.
- Hardware Tampering at Scale: More sophisticated adversaries could infiltrate hardware manufacturing processes, embedding backdoors or surveillance capabilities into devices before they even reach the end-user.
- Cloud Supply Chain Attacks: As more organizations migrate to the cloud, vulnerabilities in cloud service providers’ infrastructure or misconfigurations in their services can be exploited to compromise multiple clients simultaneously.
Protecting against Supply Chain Compromise 2.0 requires a holistic approach, extending beyond an organization’s immediate perimeter to encompass every vendor and component in its digital ecosystem. This necessitates cybersecurity software solutions with deep visibility and continuous monitoring capabilities.
3. Quantum Computing Threats to Encryption
While still in its nascent stages, the looming threat of quantum computing to current encryption standards cannot be ignored. Cryptographically relevant quantum computers (CRQCs) have the potential to break widely used public-key encryption algorithms (like RSA and ECC) that secure everything from online banking to secure communications and VPNs. While 2026 might not see widespread CRQC deployment, the preparatory attacks are already underway:
- “Harvest Now, Decrypt Later” Attacks: Adversaries are already collecting vast amounts of encrypted data today, anticipating a future where quantum computers can decrypt it. This means data considered secure now could be compromised in the future.
- Post-Quantum Cryptography (PQC) Vulnerabilities: The transition to post-quantum cryptography is complex, and early implementations or hybrid solutions could introduce new vulnerabilities that attackers will seek to exploit.
- Quantum Key Distribution (QKD) Misconfigurations: While QKD offers theoretical unbreakable encryption, its practical implementation is challenging and prone to misconfigurations that could be exploited.
Organizations must begin planning and implementing quantum-resistant cybersecurity software solutions to future-proof their data against this existential threat to modern cryptography.
Cutting-Edge Cybersecurity Software Solutions for 2026
Facing these formidable threats requires a paradigm shift in our approach to digital defense. Traditional perimeter-based security is no longer sufficient. Instead, organizations need a layered, adaptive, and intelligent security posture. Here are the essential cybersecurity software solutions forming the backbone of future-proof data protection:
1. AI-Driven Extended Detection and Response (XDR)
To combat AI-powered and autonomous attacks, organizations need equally intelligent defense systems. Extended Detection and Response (XDR) platforms, heavily augmented with AI and ML capabilities, are the answer. XDR goes beyond traditional Endpoint Detection and Response (EDR) by integrating and correlating security data from multiple layers – endpoints, network, cloud, email, and identity. This provides a holistic view of the threat landscape, enabling faster and more accurate threat detection and response.
- Predictive Threat Intelligence: AI algorithms in XDR can analyze vast datasets of threat intelligence, identifying patterns and predicting potential attack vectors before they materialize.
- Automated Anomaly Detection: Machine learning models continuously learn normal behavior within the network and flag deviations as potential threats, reducing false positives and accelerating incident response.
- Autonomous Remediation: Advanced XDR solutions can automate certain response actions, such as isolating compromised endpoints, blocking malicious IPs, or rolling back system changes, minimizing the impact of an attack.
- Behavioral Analytics: Instead of relying solely on signature-based detection, AI-driven XDR monitors user and entity behavior, identifying suspicious activities that might indicate a sophisticated, fileless attack.
Implementing AI-driven XDR is a critical investment in cybersecurity software solutions. It transforms reactive security into a proactive, intelligent defense mechanism capable of keeping pace with evolving threats.
2. Zero-Trust Architecture (ZTA) Implementations
Against the backdrop of sophisticated supply chain attacks and the erosion of traditional network perimeters, the Zero-Trust Architecture (ZTA) model has moved from a theoretical concept to an indispensable reality. The core principle of Zero Trust is “never trust, always verify.” It assumes that no user, device, or application, whether inside or outside the network, should be trusted by default. Every access request must be authenticated, authorized, and continuously validated.
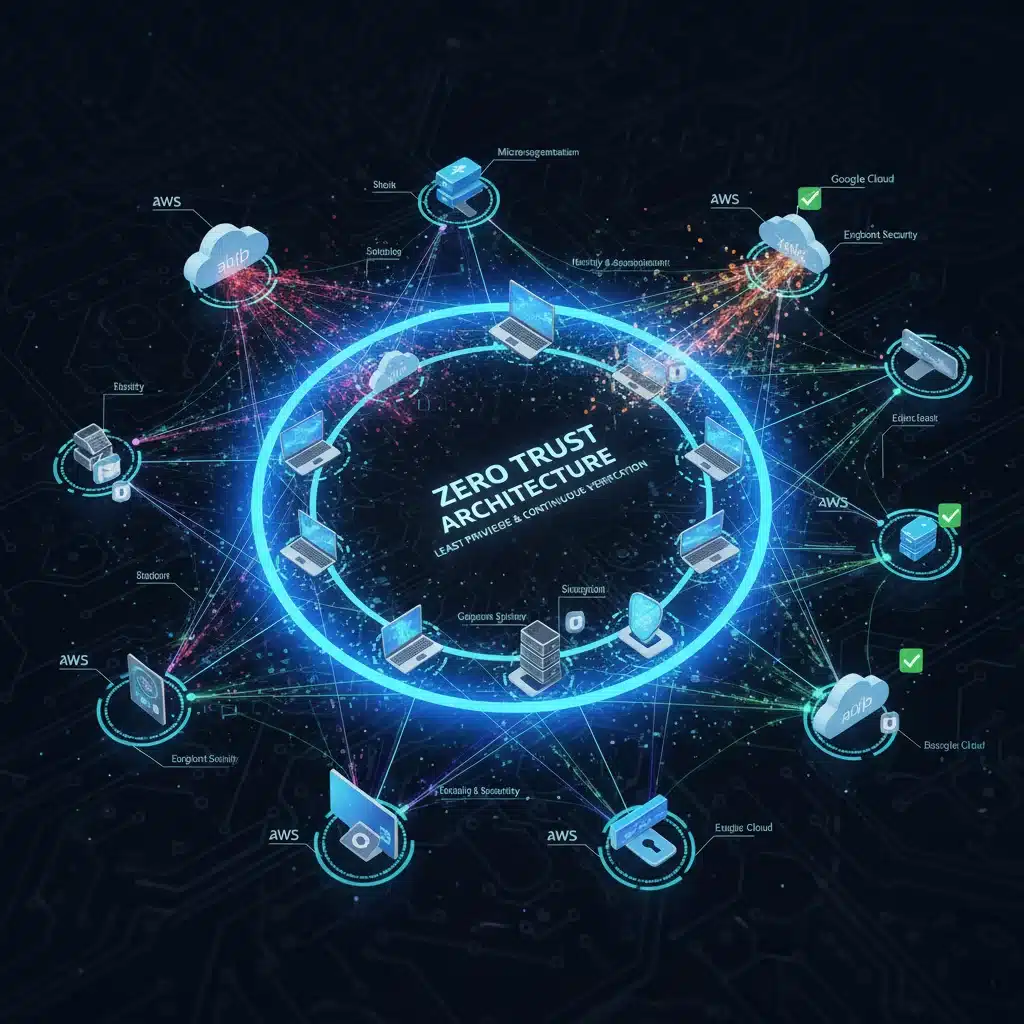
Key cybersecurity software solutions for implementing Zero Trust include:
- Identity and Access Management (IAM) with Multi-Factor Authentication (MFA): Strong IAM solutions are fundamental to ZTA, ensuring that only authenticated and authorized users can access resources. MFA adds an essential layer of security.
- Micro-segmentation: This involves dividing the network into small, isolated segments, with granular security policies applied to each segment. If one segment is compromised, the attack is contained, preventing lateral movement.
- Least Privilege Access (LPA): Users and devices are granted only the minimum access rights necessary to perform their tasks, reducing the attack surface.
- Continuous Monitoring and Validation: Security software continuously monitors all traffic and activity, verifying user identities, device posture, and application behavior in real-time. Any deviation triggers re-authentication or denial of access.
- Secure Access Service Edge (SASE) Platforms: SASE converges network security functions (like firewalls, secure web gateways, and zero-trust network access) with WAN capabilities into a single, cloud-native service, simplifying ZTA deployment for distributed workforces.
Zero Trust is not a single product but a strategic approach supported by a suite of integrated cybersecurity software solutions. Its implementation drastically reduces the impact of breaches by limiting an attacker’s ability to move freely within a compromised environment.
3. Post-Quantum Cryptography (PQC) & Cryptographic Agility Tools
Addressing the quantum computing threat requires a forward-looking strategy focused on Post-Quantum Cryptography (PQC). PQC refers to cryptographic algorithms that are believed to be secure against attacks by quantum computers. While the full impact of quantum computing may be years away, the “harvest now, decrypt later” threat means organizations must start preparing today.
Essential cybersecurity software solutions in this domain include:
- PQC Algorithm Implementation Kits: Software development kits (SDKs) and libraries that allow developers to integrate new, quantum-resistant cryptographic algorithms into their applications and systems.
- Cryptographic Agility Management Platforms: Tools that enable organizations to easily switch between different cryptographic algorithms (including PQC candidates) without major system overhauls. This agility is crucial as the PQC landscape evolves and new standards emerge.
- Quantum-Safe VPNs and Communication Protocols: Upgraded VPNs and secure communication channels that utilize PQC algorithms to protect data in transit from future quantum attacks.
- Inventory and Discovery Tools for Cryptographic Assets: Software that helps organizations identify all cryptographic assets (keys, certificates, encrypted data) across their infrastructure, which is essential for planning a PQC migration.
- Homomorphic Encryption Software: While not strictly PQC, homomorphic encryption allows computations on encrypted data without decrypting it, offering a unique layer of privacy and security against various threats, including potential quantum decryption of data in use.
The transition to PQC is a monumental undertaking, but cryptographic agility and the adoption of PQC-ready cybersecurity software solutions are vital steps to ensure long-term data confidentiality and integrity.
Integrating Cybersecurity Software Solutions for a Unified Defense
The strength of your cybersecurity posture in 2026 will not just depend on individual cybersecurity software solutions but on how effectively they are integrated into a cohesive, unified defense system. A fragmented approach, where security tools operate in silos, creates gaps that sophisticated attackers can exploit. The goal is to create a symbiotic relationship between different security layers, allowing them to share intelligence and coordinate responses seamlessly.
Security Information and Event Management (SIEM) & Security Orchestration, Automation, and Response (SOAR)
At the heart of an integrated security ecosystem are SIEM and SOAR platforms. SIEM solutions collect and analyze security logs and event data from across the entire IT infrastructure, providing a centralized view of security events. While SIEM identifies threats, SOAR takes it a step further by orchestrating and automating security operations. It integrates with various cybersecurity software solutions to streamline incident response workflows, reduce manual tasks, and accelerate threat containment.
- Centralized Visibility: SIEM aggregates data from XDR, IAM, network devices, and cloud logs, offering a comprehensive overview of security status.
- Automated Playbooks: SOAR uses predefined playbooks to automate responses to common threats, such as phishing attacks or malware infections, freeing up security analysts for more complex tasks.
- Enhanced Collaboration: By automating routine tasks and centralizing information, SIEM and SOAR improve collaboration among security teams and with other IT departments.
Threat Intelligence Platforms (TIPs)
Effective cybersecurity software solutions are not just about defense; they’re also about intelligence. Threat Intelligence Platforms (TIPs) collect, process, and analyze vast amounts of threat data from various sources – open-source intelligence, dark web monitoring, industry feeds, and proprietary research. This intelligence provides context to security events, helping organizations understand who is attacking them, why, and how.
- Proactive Defense: By understanding emerging threats, organizations can proactively adjust their cybersecurity software solutions and defenses.
- Contextual Awareness: TIPs enrich security alerts with crucial context, allowing security teams to prioritize and respond to the most critical threats first.
- Indicator of Compromise (IoC) Sharing: TIPs facilitate the sharing of IoCs (e.g., malicious IP addresses, file hashes) across security tools, enabling faster detection and blocking of known threats.
Cloud Security Posture Management (CSPM) & Cloud Workload Protection Platforms (CWPP)
As cloud adoption accelerates, ensuring the security of cloud environments becomes paramount. CSPM solutions continuously monitor cloud configurations for misconfigurations and compliance violations, which are a leading cause of cloud breaches. CWPPs, on the other hand, focus on protecting workloads (virtual machines, containers, serverless functions) running in the cloud, offering features like vulnerability management, runtime protection, and host intrusion detection.
- Continuous Compliance: CSPM ensures that cloud environments adhere to regulatory requirements and best practices.
- Workload Hardening: CWPPs provide granular control and protection for individual cloud workloads, regardless of their location.
- Visibility into Cloud Assets: These cybersecurity software solutions offer deep visibility into cloud assets, helping organizations understand their attack surface in dynamic cloud environments.
The Human Element: Training and Awareness
Even the most advanced cybersecurity software solutions can be undermined by human error. In 2026, with the rise of sophisticated deepfake phishing and social engineering attacks, the human element remains a critical vulnerability. Therefore, ongoing security awareness training and education are not just beneficial but absolutely essential.
- Regular Training Modules: Implement interactive and engaging training programs that cover the latest threats, including AI-powered social engineering tactics.
- Simulated Phishing Campaigns: Regularly test employees with realistic phishing and deepfake simulations to reinforce training and identify areas for improvement.
- Culture of Security: Foster a workplace culture where security is everyone’s responsibility, and employees feel empowered to report suspicious activities without fear of reprisal.
Investing in cybersecurity software solutions without simultaneously investing in human training is like building a fortress with an open drawbridge. Both are vital components of a robust defense.
Conclusion: A Proactive Stance with Advanced Cybersecurity Software Solutions
The year 2026 promises a highly challenging cybersecurity landscape, dominated by AI-powered attacks, pervasive supply chain compromises, and the looming threat of quantum decryption. Organizations that fail to adapt their defense strategies risk significant financial, reputational, and operational damage. The key to resilience lies in adopting a proactive, layered, and intelligent security posture, underpinned by cutting-edge cybersecurity software solutions.
By implementing AI-driven XDR for comprehensive threat detection and response, embracing Zero-Trust Architecture for granular access control, and preparing for quantum threats with PQC and cryptographic agility tools, businesses can build a formidable defense. Furthermore, integrating these solutions with SIEM/SOAR platforms, leveraging threat intelligence, and securing cloud environments with CSPM/CWPP will create a unified, resilient security ecosystem. Remember, technology alone is not enough; continuous employee training and a strong security culture are equally vital components.
The future of cybersecurity is not about preventing every single attack – an impossible feat – but about building resilience, minimizing impact, and ensuring rapid recovery. Investing wisely in the right cybersecurity software solutions today will determine the security of your data tomorrow.