Cybersecurity Frameworks for SMBs in 2026: Reducing Breach Risks by 20% with Updated NIST Guidelines
Anúncios
In an increasingly digital landscape, the threat of cyberattacks looms larger than ever, particularly for Small and Medium-sized Businesses (SMBs). Often perceived as less fortified targets than their enterprise counterparts, SMBs are, in reality, highly susceptible to cyber breaches due to limited resources, lack of dedicated cybersecurity personnel, and a misconception that they are not attractive targets. The financial and reputational repercussions of a successful cyberattack can be devastating, with many SMBs struggling to recover. This is where robust SMB Cybersecurity Frameworks become not just beneficial, but absolutely essential for survival and growth in the modern economy.
Anúncios
The year 2026 is rapidly approaching, and with it, an imperative for SMBs to proactively strengthen their cyber defenses. Our goal today is to delve into how updated NIST guidelines can serve as a cornerstone for these efforts, aiming for a tangible 20% reduction in breach risks. This article will provide a comprehensive guide, offering actionable insights and strategies for implementing effective cybersecurity frameworks tailored to the unique challenges and opportunities faced by SMBs.
Understanding the current threat landscape is the first step toward building resilience. Cybercriminals are becoming more sophisticated, employing advanced phishing techniques, ransomware, and supply chain attacks that specifically target vulnerabilities within smaller organizations. The average cost of a data breach for SMBs continues to rise, making preventative measures a sound investment rather than an optional expense. By adopting structured SMB Cybersecurity Frameworks, businesses can move beyond reactive security measures to a proactive, risk-informed approach that safeguards their assets, customer data, and reputation.
Anúncios
This article will explore the evolution of cybersecurity threats, the specific challenges SMBs face, and most importantly, how the National Institute of Standards and Technology (NIST) Cybersecurity Framework, with its latest updates, provides a scalable and adaptable blueprint for enhancing security posture. We will break down the core components of the NIST framework, discuss practical implementation strategies, and highlight key considerations for SMBs aiming to achieve a significant reduction in breach risks by 2026. Join us as we navigate the complexities of modern cybersecurity and empower your business with the knowledge and tools to thrive securely.
The Evolving Cyber Threat Landscape for SMBs
The digital world offers unparalleled opportunities for growth, but it also presents an ever-evolving array of threats. For SMBs, these threats are particularly insidious. Unlike large corporations with extensive IT departments and multi-million dollar security budgets, SMBs often operate with lean teams, generalist IT staff, or even outsourced IT services that may not specialize in advanced cybersecurity. This resource disparity makes them attractive targets for cybercriminals who view them as ‘low-hanging fruit’ – easier to compromise and often holding valuable data.
Common Attack Vectors Targeting SMBs
- Phishing and Social Engineering: These remain the most prevalent attack methods. Cybercriminals craft convincing emails or messages designed to trick employees into revealing sensitive information, clicking malicious links, or downloading malware. For SMBs, where employees often wear multiple hats and may not receive regular, in-depth security training, these attacks are highly effective.
- Ransomware: This malicious software encrypts a victim’s files, demanding a ransom payment (usually in cryptocurrency) for their release. Ransomware attacks can cripple an SMB’s operations, leading to significant downtime, data loss, and severe financial strain. The healthcare and manufacturing sectors, often populated by SMBs, have been particularly hard hit.
- Supply Chain Attacks: Attackers compromise a less secure vendor or partner of a larger organization to gain access to the larger target. SMBs often serve as crucial links in larger supply chains, making them indirect targets that can lead to widespread disruption.
- Business Email Compromise (BEC): Fraudsters impersonate executives or trusted partners to trick employees into transferring funds or sensitive data. These attacks are highly sophisticated and often rely on extensive research into the target company.
- Insider Threats: While often unintentional, employees can inadvertently cause security incidents through negligence, poor security practices, or falling victim to phishing. Malicious insider threats, though rarer, can also lead to significant data theft or system sabotage.
Why SMBs Are Prime Targets
Beyond the resource limitations, several factors contribute to SMBs being prime targets:
- Valuable Data: SMBs handle a wealth of sensitive data, including customer information, financial records, intellectual property, and employee data, all of which are attractive to cybercriminals.
- Lack of Awareness: Many SMB owners and employees underestimate the risk of a cyberattack, believing they are too small to be targeted. This lack of awareness often translates into inadequate security measures.
- Outdated Systems: Budget constraints can lead to delayed hardware and software upgrades, leaving systems vulnerable to known exploits.
- Limited Expertise: Without dedicated cybersecurity professionals, SMBs often lack the specialized knowledge required to identify, prevent, and respond to sophisticated threats.
The financial impact of a breach extends far beyond the immediate costs of remediation. It includes reputational damage, loss of customer trust, regulatory fines (especially with data protection laws like GDPR and CCPA), and potential legal fees. For an SMB, these combined costs can be catastrophic, leading to business closure in some cases. This stark reality underscores the urgency for SMBs to adopt robust SMB Cybersecurity Frameworks that can effectively mitigate these growing risks.
Introducing the NIST Cybersecurity Framework (CSF) for SMBs
The National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) is a voluntary framework consisting of standards, guidelines, and best practices to manage cybersecurity risk. While initially developed for critical infrastructure, its flexible and scalable nature makes it an invaluable tool for organizations of all sizes, especially SMBs looking to enhance their cyber posture without overwhelming their limited resources.
What is the NIST CSF?
The NIST CSF provides a common language and systematic approach for organizations to:
- Understand and manage their cybersecurity risks.
- Communicate cybersecurity risk to internal and external stakeholders.
- Implement or improve their cybersecurity programs.
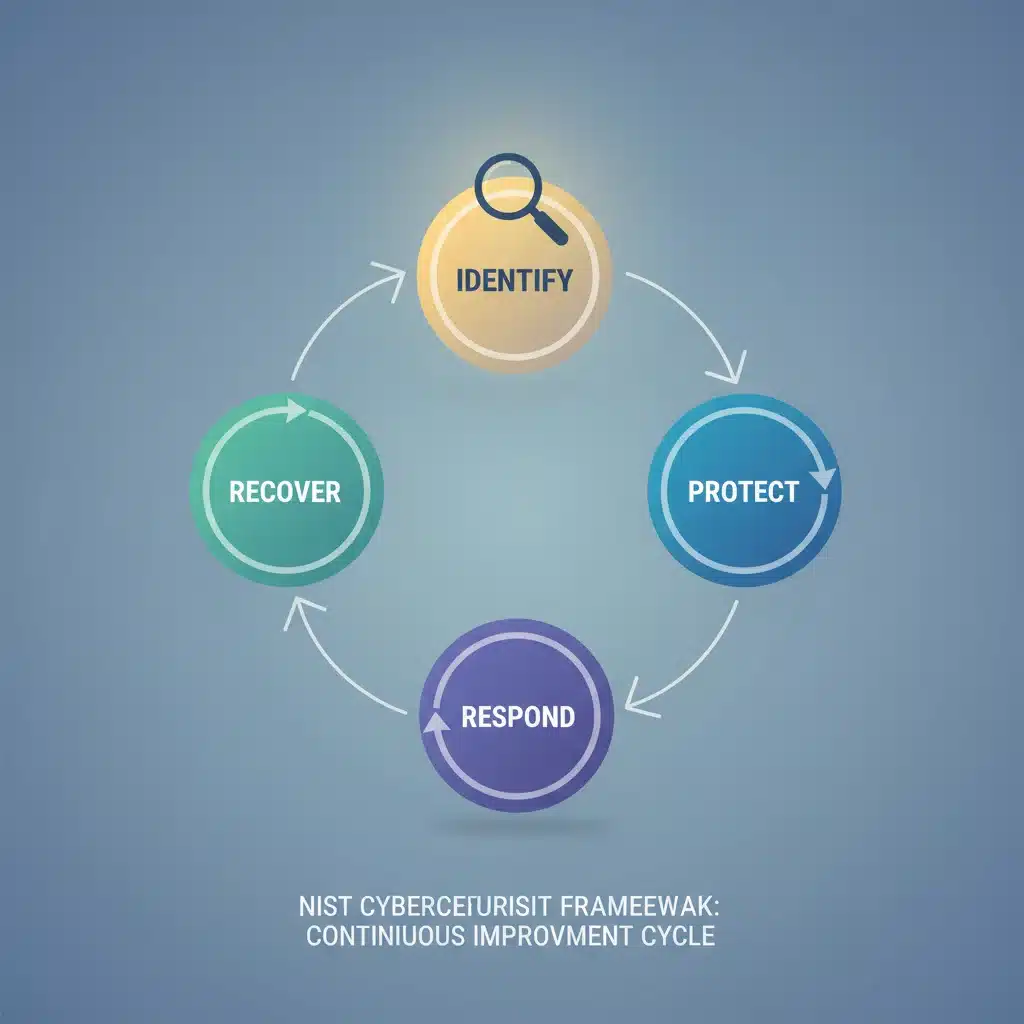
It is not a one-size-fits-all solution, but rather a flexible framework that can be adapted to an organization’s specific needs, risk tolerance, and resources. The CSF is structured around five core functions, which provide a high-level strategic view of an organization’s management of cybersecurity risk:
- Identify: Develop an organizational understanding to manage cybersecurity risk to systems, assets, data, and capabilities.
- Protect: Develop and implement appropriate safeguards to ensure delivery of critical services.
- Detect: Develop and implement appropriate activities to identify the occurrence of a cybersecurity event.
- Respond: Develop and implement appropriate activities to take action regarding a detected cybersecurity incident.
- Recover: Develop and implement appropriate activities to maintain plans for resilience and to restore any capabilities or services that were impaired due to a cybersecurity incident.
Why NIST CSF is Ideal for SMBs
Many SMBs shy away from formal cybersecurity frameworks, fearing complexity and cost. However, the NIST CSF is particularly well-suited for SMBs for several reasons:
- Flexibility and Scalability: The framework is designed to be adaptable. SMBs can start with a basic implementation focusing on their most critical assets and gradually expand as their understanding and resources grow. It doesn’t prescribe specific technologies but rather outcomes.
- Risk-Based Approach: Instead of a prescriptive checklist, the NIST CSF encourages a risk-based approach. SMBs can prioritize their cybersecurity investments based on their unique risk profile, ensuring that resources are allocated effectively to address the most significant threats.
- Common Language: It provides a standardized language for discussing cybersecurity, which can help SMBs communicate more effectively with vendors, insurance providers, and even customers about their security posture.
- Industry Recognition: The NIST CSF is widely recognized and respected, offering a credible benchmark for demonstrating due diligence in cybersecurity. This can be beneficial for compliance, insurance, and customer assurance.
- Continuous Improvement: The framework promotes a continuous improvement cycle, encouraging organizations to regularly assess their cybersecurity posture, identify gaps, and implement enhancements. This iterative process is crucial in a rapidly changing threat landscape.
The latest updates to the NIST CSF (e.g., CSF 2.0) further emphasize governance, supply chain risk management, and measuring outcomes, making it even more relevant for SMBs navigating complex digital ecosystems. By embracing the NIST CSF as their guiding SMB Cybersecurity Framework, small and medium businesses can systematically build a strong defense, moving towards the ambitious goal of reducing breach risks by 20% by 2026.
Updated NIST Guidelines for 2026: Key Changes and Their Impact on SMBs
The cybersecurity landscape is dynamic, and frameworks must evolve to remain effective. The NIST Cybersecurity Framework (CSF) undergoes periodic updates to address emerging threats, technologies, and best practices. While specific details for 2026 might involve continuous refinements, the general direction of updates emphasizes a more holistic, enterprise-wide approach to risk management, with a stronger focus on governance, supply chain, and measurement. Understanding these shifts is crucial for SMBs to adapt their SMB Cybersecurity Frameworks effectively.
Key Areas of Focus in Recent and Anticipated NIST CSF Updates:
- Enhanced Governance: Recent updates, like CSF 2.0, place a greater emphasis on the ‘Govern’ function. This means cybersecurity is no longer just an IT issue but a fundamental business risk that requires attention from leadership. For SMBs, this translates to:
- Board/Leadership Engagement: Even without a formal board, owners and senior management must actively participate in cybersecurity strategy, resource allocation, and risk acceptance.
- Defined Roles and Responsibilities: Clearly assigning who is responsible for what in cybersecurity, even if it’s an IT manager wearing multiple hats or an outsourced provider.
- Policy Development: Establishing clear, documented policies for cybersecurity, data handling, and incident response.
- Supply Chain Risk Management (SCRM): The increasing prevalence of supply chain attacks has made SCRM a critical component. SMBs are often part of larger supply chains, making them both potential victims and vectors for attacks. Updates stress:
- Vendor Risk Assessments: Evaluating the cybersecurity posture of third-party vendors and partners.
- Contractual Clauses: Including cybersecurity requirements in contracts with suppliers and customers.
- Monitoring Third-Party Access: Managing and monitoring access granted to external parties.
- Measurement and Outcomes: There’s a growing need to demonstrate the effectiveness of cybersecurity investments. Updated guidelines encourage organizations to:
- Define Metrics: Establish clear metrics to measure the effectiveness of cybersecurity controls.
- Regular Assessments: Conduct periodic assessments to identify gaps and track progress.
- Reporting: Communicate cybersecurity performance and risk posture to management.
- Increased Focus on Automation and AI: While not explicitly a CSF function, the underlying technologies that support effective cybersecurity are evolving. SMBs should consider how automation and AI-powered tools can augment their limited human resources for threat detection, vulnerability management, and incident response.
- Human Element and Culture: Acknowledging that people are often the weakest link, the updates implicitly reinforce the importance of security awareness training and fostering a security-first culture within the organization.
Impact on SMBs: Adapting Your Cybersecurity Strategy
These updated guidelines offer both challenges and opportunities for SMBs:
- Opportunity for Proactive Security: By embracing the ‘Govern’ function, SMBs can embed cybersecurity into their business strategy, moving from reactive firefighting to proactive risk management.
- Stronger Partnerships: Enhanced SCRM can lead to more secure and trustworthy relationships with vendors and clients, potentially opening doors to new business opportunities that require strong cybersecurity assurances.
- Justifying Investment: The emphasis on measurement provides SMBs with the tools to demonstrate the ROI of cybersecurity investments, making it easier to secure budget and resources.
- Leveraging Scalable Solutions: The framework’s flexibility allows SMBs to adopt cloud-based security services and managed security service providers (MSSPs) that can help them meet these updated requirements without significant in-house investment.
By understanding and proactively incorporating these updated NIST guidelines into their SMB Cybersecurity Frameworks, businesses can significantly enhance their resilience against cyber threats, getting closer to the 20% breach risk reduction target by 2026. It’s about smart, strategic security that grows with the business, rather than being an afterthought.
Practical Implementation Strategies for SMBs
Implementing a comprehensive SMB Cybersecurity Framework based on NIST guidelines doesn’t have to be an insurmountable task. For small and medium-sized businesses, the key is to adopt a phased, prioritized approach that aligns with their specific risk profile, resources, and business objectives. Here are practical strategies to get started and make tangible progress towards reducing breach risks by 20% by 2026.
1. Start with the ‘Identify’ Function: Know What You’re Protecting
This is arguably the most critical first step. You can’t protect what you don’t know you have. For SMBs, this involves:
- Asset Inventory: Create a comprehensive list of all IT assets – hardware (servers, workstations, mobile devices), software (operating systems, applications), data (customer, financial, IP), and services (cloud platforms, SaaS). Understand where your critical data resides.
- Business Environment Understanding: Document your business processes and how technology supports them. Identify the impact if a particular system or data set becomes unavailable or compromised.
- Risk Assessment: Conduct a simplified risk assessment. Identify potential threats (e.g., ransomware, phishing) and vulnerabilities (e.g., outdated software, lack of employee training). Prioritize risks based on likelihood and impact.
- Governance and Policies: Establish basic cybersecurity policies, even if informal initially. Who is responsible for what? What are the rules for password management, data access, and remote work?
2. Focus on ‘Protect’ – Essential Safeguards
Once you know your assets and risks, implement foundational protections:
- Access Control: Implement strong password policies, multi-factor authentication (MFA) for all critical systems (email, cloud services, VPN), and least privilege access (employees only access what they need).
- Security Awareness Training: Regular, engaging training for all employees on phishing, social engineering, and safe online practices. This is your most cost-effective defense.
- Data Security: Encrypt sensitive data both in transit and at rest. Implement regular data backups and test their restorability.
- Protective Technology: Deploy firewalls, antivirus/anti-malware software, and intrusion prevention systems. Ensure all software and operating systems are regularly patched and updated.
- Secure Configurations: Ensure all devices and applications are configured securely, disabling unnecessary services and ports.
3. Implement ‘Detect’ – Early Warning Systems
Even with strong protections, breaches can occur. Early detection is vital for minimizing damage:
- Monitoring: Implement basic logging and monitoring of network activity, system events, and user access. Look for unusual patterns.
- Vulnerability Scanning: Conduct regular (even basic) scans to identify vulnerabilities in your systems and applications.
- Threat Intelligence: Stay informed about common threats targeting SMBs in your industry.
4. Prepare for ‘Respond’ – Incident Response Plan
A well-defined incident response plan can significantly reduce the impact of a breach:
- Plan Development: Create a simple, documented plan outlining steps to take during a cyber incident (e.g., who to contact, how to isolate affected systems, how to communicate).
- Communication Plan: Identify key stakeholders (employees, customers, legal, PR) and how you will communicate with them during an incident.
- Practice and Test: Periodically test your incident response plan through tabletop exercises to identify gaps and refine procedures.
5. Plan for ‘Recover’ – Business Continuity
Being able to restore operations quickly after an incident is paramount:
- Backup and Recovery: Ensure robust, tested backup and recovery procedures are in place. Store backups offsite and offline where possible.
- Business Continuity Planning: Understand critical business functions and how to maintain them during and after a cyber incident.
- Lessons Learned: After any incident (even minor ones), conduct a post-mortem to identify what went well and what could be improved.
Leveraging External Resources
SMBs don’t have to go it alone:
- Managed Security Service Providers (MSSPs): Consider outsourcing some cybersecurity functions to an MSSP. They can provide expertise, monitoring, and incident response capabilities that SMBs often lack in-house.
- Cloud Security: Utilize the built-in security features of cloud service providers (AWS, Azure, Google Cloud). They often offer advanced security controls that would be cost-prohibitive for SMBs to implement on-premises.
- Government Resources: Agencies like NIST, CISA (Cybersecurity and Infrastructure Security Agency), and local government programs often provide free resources, guides, and tools for SMBs.
By systematically addressing each of these functions, SMBs can build a robust and resilient SMB Cybersecurity Framework. The goal isn’t perfection from day one, but continuous improvement and a commitment to making cybersecurity an integral part of business operations. This strategic approach will be instrumental in achieving the 20% reduction in breach risks by 2026.
Measuring Success: Achieving a 20% Reduction in Breach Risks by 2026
Setting a target of a 20% reduction in breach risks by 2026 is ambitious yet achievable for SMBs committed to implementing robust SMB Cybersecurity Frameworks. However, simply implementing controls isn’t enough; true success lies in the ability to measure progress, identify areas for improvement, and demonstrate the tangible impact of cybersecurity investments. This section will outline how SMBs can effectively measure their cybersecurity posture and track their journey towards this critical goal.
Defining ‘Breach Risk Reduction’ for SMBs
For SMBs, ‘breach risk reduction’ can be quantified in several ways, moving beyond just the number of successful attacks. It encompasses:
- Reduced Incident Frequency: A decrease in the number of successful cyberattacks or security incidents over time.
- Reduced Incident Severity: When incidents do occur, their impact (e.g., data compromised, downtime, financial loss) is less severe due to effective controls and rapid response.
- Improved Detection Time: The time it takes to detect a malicious activity or breach is significantly shortened.
- Faster Recovery Time: The ability to restore operations and data quickly after an incident.
- Increased Compliance & Trust: Better adherence to industry standards and regulatory requirements, leading to greater customer and partner trust.
Key Metrics and KPIs for SMBs
SMBs should focus on practical, actionable metrics that don’t require overly complex tools. Here are some key performance indicators (KPIs) to track:
- Security Awareness Training Completion Rates: High completion rates indicate employee engagement, which directly impacts the human firewall.
- Phishing Click-Through Rates: A decreasing trend in employees clicking on simulated phishing emails signifies improved awareness and caution.
- Vulnerability Scan Results: Tracking the number of critical and high-severity vulnerabilities discovered and, more importantly, the time taken to remediate them.
- MFA Adoption Rate: The percentage of users and critical systems protected by multi-factor authentication.
- Patch Management Compliance: The percentage of systems updated with the latest security patches within a defined timeframe.
- Backup Success & Restoration Test Rates: Ensuring backups are consistently successful and can be reliably restored.
- Incident Response Time: The average time from detection of an incident to its containment.
- Number of Security Incidents: Tracking the total number of security events and distinguishing between attempted attacks and successful breaches.
- Third-Party Vendor Security Scorecards: If applicable, tracking the security posture of critical vendors.
Tools and Techniques for Measurement
SMBs can leverage various tools and techniques to collect and analyze these metrics:
- Security Information and Event Management (SIEM) Lite Solutions: Scaled-down SIEMs or log management tools can help aggregate security logs for easier analysis.
- Vulnerability Scanners: Automated tools that identify weaknesses in systems and applications.
- Phishing Simulation Platforms: Services that allow SMBs to test employee susceptibility to phishing attacks.
- Endpoint Detection and Response (EDR) Tools: Solutions that provide visibility into endpoint activity and can help detect and respond to threats.
- Regular Audits and Assessments: Conducting internal or external cybersecurity audits to get an objective view of your security posture.
- NIST CSF Self-Assessment Tools: NIST provides guidance and templates for organizations to self-assess their alignment with the framework.
Continuous Improvement Cycle
Achieving the 20% reduction is not a one-time event but an ongoing process. SMBs should adopt a continuous improvement cycle:
- Assess: Regularly evaluate your current cybersecurity posture using the defined metrics.
- Identify Gaps: Pinpoint areas where your controls are weak or where risks are not adequately mitigated.
- Plan: Develop strategies and actions to address identified gaps, prioritizing based on risk.
- Implement: Deploy new controls, update policies, or conduct additional training.
- Monitor: Continuously track your metrics to see the impact of your changes.
- Review: Periodically review your entire SMB Cybersecurity Framework to ensure it remains relevant and effective against evolving threats.
By systematically applying these measurement strategies, SMBs can gain clear insights into their cybersecurity strengths and weaknesses, make data-driven decisions, and confidently work towards the goal of significantly reducing their breach risks by 2026. This proactive, measurable approach transforms cybersecurity from a daunting expense into a strategic investment that safeguards the business’s future.
Conclusion: Securing the Future of SMBs with NIST
The digital economy offers unprecedented opportunities for growth and innovation, yet it simultaneously exposes Small and Medium-sized Businesses (SMBs) to an ever-present and escalating threat of cyberattacks. As we look towards 2026, the imperative for SMBs to adopt robust SMB Cybersecurity Frameworks has never been more critical. The goal of achieving a 20% reduction in breach risks is not merely aspirational; it is a vital step towards ensuring business continuity, protecting valuable assets, and maintaining customer trust in an increasingly interconnected world.
Throughout this article, we’ve explored the unique challenges SMBs face in the dynamic cyber threat landscape, from sophisticated phishing campaigns to crippling ransomware attacks. We’ve established that the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) is not just for large enterprises but offers a flexible, scalable, and risk-based blueprint perfectly suited for SMBs. The updated NIST guidelines, with their enhanced focus on governance, supply chain risk management, and outcome measurement, provide an even stronger foundation for modern cybersecurity practices.
Our practical implementation strategies have demonstrated that securing your business doesn’t require an astronomical budget or an army of cybersecurity experts. By systematically addressing the five core functions of the NIST CSF – Identify, Protect, Detect, Respond, and Recover – SMBs can build a resilient defense. Simple yet effective measures like comprehensive asset inventories, regular employee security awareness training, multi-factor authentication, robust backup solutions, and a clear incident response plan can significantly elevate an SMB’s security posture. Furthermore, leveraging external resources such as Managed Security Service Providers (MSSPs) and cloud security features can bridge the expertise and resource gaps often faced by smaller organizations.
Crucially, we’ve emphasized the importance of measurement. Achieving a 20% reduction in breach risks by 2026 requires more than just implementing controls; it demands continuous monitoring, evaluation, and adaptation. By tracking key performance indicators (KPIs) like phishing click-through rates, vulnerability remediation times, and incident response metrics, SMBs can gain actionable insights, justify their security investments, and demonstrate tangible progress. This iterative approach ensures that cybersecurity remains a living, evolving part of the business strategy, rather than a static, one-time fix.
In conclusion, the future success and resilience of SMBs are inextricably linked to their cybersecurity maturity. By embracing the NIST Cybersecurity Framework as their guiding SMB Cybersecurity Framework, small and medium-sized businesses can transform their approach to security from a reactive burden to a proactive, strategic advantage. The journey to a 20% reduction in breach risks by 2026 is a commitment to safeguarding your business, your data, and your reputation. Start today, stay vigilant, and build a more secure tomorrow.